I would say that the ideal password is simple and, at the same time, secure. And what fits that definition can change depending on the context. Listen to me.
Welcome to Safe Mode, your weekly briefing with urgent security and privacy news, and what to do next. Want this newsletter delivered straight to your inbox? Register on our website!
In some cases, the ideal password is actually a passcode. (So it’s not a password at all.) They are the epitome of simple and safe. Memory-free and non-reusable, with integrated two-factor authentication elements. For these reasons, I recommend using it first for most people.
Meanwhile, for websites that lack passkey support, an ideal password is something long, random, and unique—something that is easily generated and stored by a password manager. You’ll spend just as little effort on a 32-character password as you will on an 8-character version.
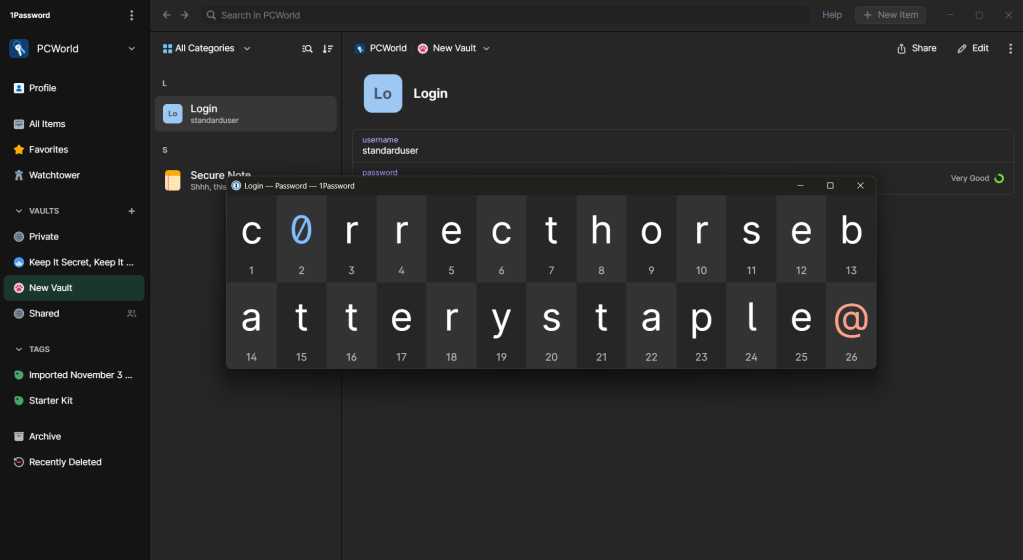
But what happens when you really have to memorize a password? My opinion has changed mainly in terms of approach here. You should memorize at least a few: at least two passwords, one for your password manager and the other for your email address. You don’t want to be left without access to your email address or another important account (for example, bank) because you lost access to your password manager.
However, doing so should not be difficult. I used to similarly suggest passphrases and pseudorandomization (e.g. extracting the second letter of a song lyric you know and interspersing numbers and special characters). I’m much more into the passphrase camp now. The longer the better. If you are able to memorize a random combination of words, you will get bonus points.
What made me change my mind: look at the password cracking tables one more time.