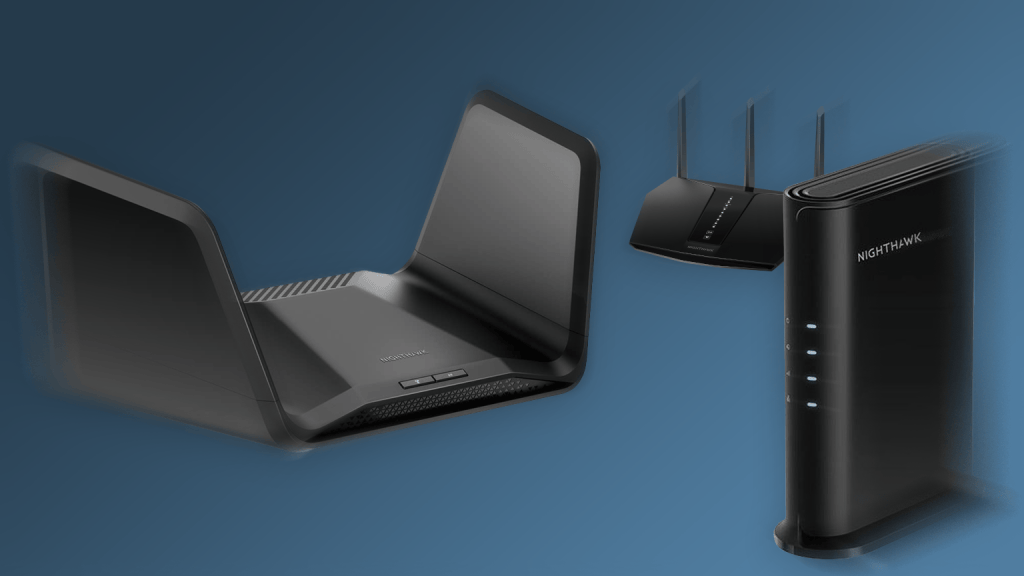
Another vulnerability (CVE-2026-11731) affects the RAX28, RAX29 and RAX30 models. This allows an attacker with local access to the router’s management interface to bypass login and modify certain settings.
Meanwhile, Netgear Wi-Fi extender models EX3700 and EX6120 are also affected by a vulnerability (CVE-2026-11730) that could be exploited to hijack a logged-in administrator session.
Netgear has released updates for affected models and recommends that users install the latest firmware as soon as possible. The company also urges users to enable automatic updates whenever possible.
Other vulnerabilities were also included in the security advisory, including CVE-2026-9218, CVE-2026-107918, and CVE-2026-107917. These only affect models that are no longer supported, such as the R7000, RAX40 and R7300DST. All unsupported models, including RAX5 and EX3700, will no longer receive security updates. In such cases, Netgear recommends replacing them with newer products.