This is not about rogue AI agents talking about your private data. Instead, the culprit is a much older digital tool, an ordinary URL.
Welcome to another edition of Prompt Mode, your weekly AI newsletter.
I’m your host, Ben Patterson. Every week in Quick modeI will offer analysis of AI trends that matter to everyday users like you and me. Stay tuned for practical AI tips, hands-on experiences with the latest AI tools, and, you guessed it, pointers to help you get the most out of your AI assistants.
Thanks for reading, and if you like what you see, just register here.
In the latest incident, Claroc privacy researchers found that it took a single DNS query to detect more than 6,000 shared Muse chats, including conversations with data as sensitive as a small business loan application, partial bank account numbers, lists of employee names, and internal business reports riddled with PII (personally identifiable information) and raw revenue figures.
It turns out that the problem was Meta’s decision to use the chat title within the web address, making it easier to find shared conversations using a passive DNS lookup.
Meta removed Muse’s sharing feature shortly after Claroc researchers informed them of the breach pending “changes to how these links can be discovered.”
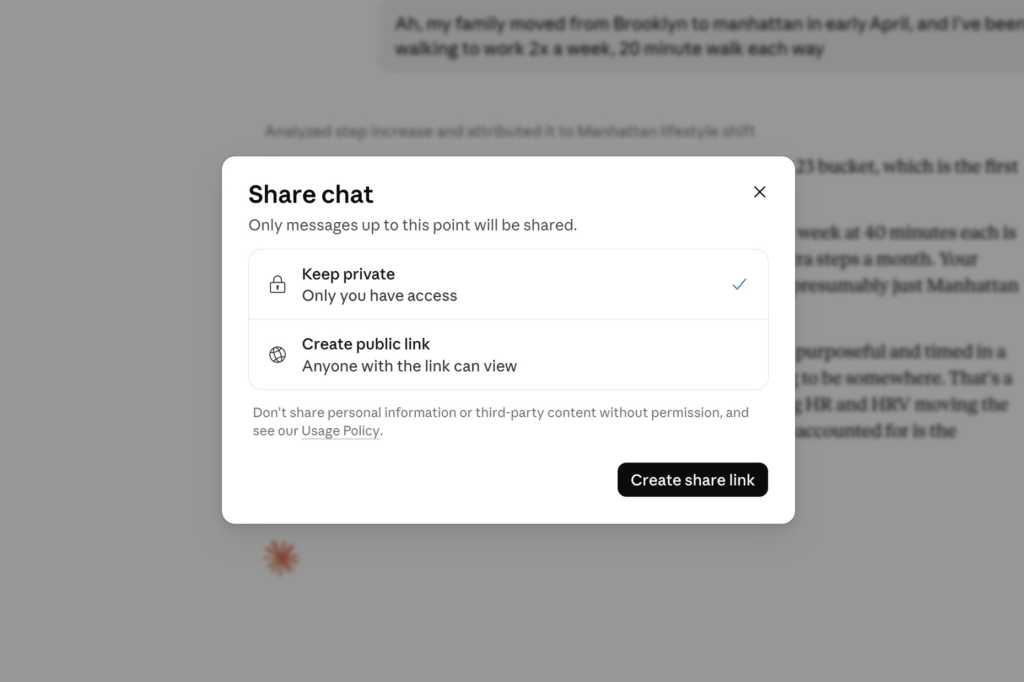
Muse users aren’t the only ones seeing their AI chats exposed on the internet. Last summer, several Claude users were rudely surprised when their shared conversations appeared in Google search results, a repeat of a similar episode last September. Early last year, some ChatGPT users discovered that their AI chats were also searchable on Google. In each of those cases, the shared AI conversations were eventually removed from Google search.
While the details of the Meta Muse incident are different from the ChatGPT and Claude cases (Muse’s chats were exposed via DNS queries, while Google traced ChatGPT and Claude’s threads), they all stem from a common vulnerability.